

Every vendor relationship, tracked from first look to offboarding
A weighted evaluation for new vendors, then scorecards, reviews and obligations for the ones you keep, in one searchable directory.
Every vendor you work with, in one list
Not a folder of contracts — the vendor itself, as its own record. Every relationship your org has is searchable and filterable by capability, segment, and health, with every contract tied to that vendor rolled up underneath it.
Click into any vendor and see its full history in one place — every contract, every health check, every certification — instead of piecing it together from separate records.
A scorecard before you commit to a first-timer
A brand-new vendor and a routine renewal are not the same risk. Granur treats them differently by design — a first-time vendor gets a weighted evaluation across eight dimensions (strategic fit, capability, architecture, data, security, performance, commercial, and vendor model), plus mandatory pass/fail gates and a strategic-risk read on ecosystem fit and exit cost, the moment it's flagged "new" at intake; a renewal doesn't, because that relationship has already been vetted.
Evaluation scorecard, Vendor Risk Assessment, and privacy / AI diligence all apply — the relationship is unproven, so the gates run in full.
No evaluation scorecard and no re-run of diligence already on file. The focus shifts to negotiation — terms, pricing, and renewal timing.
Weighted rubric for onboarding a new vendor — separate from the VRA / compliance gates.
A portfolio view, not one vendor at a time
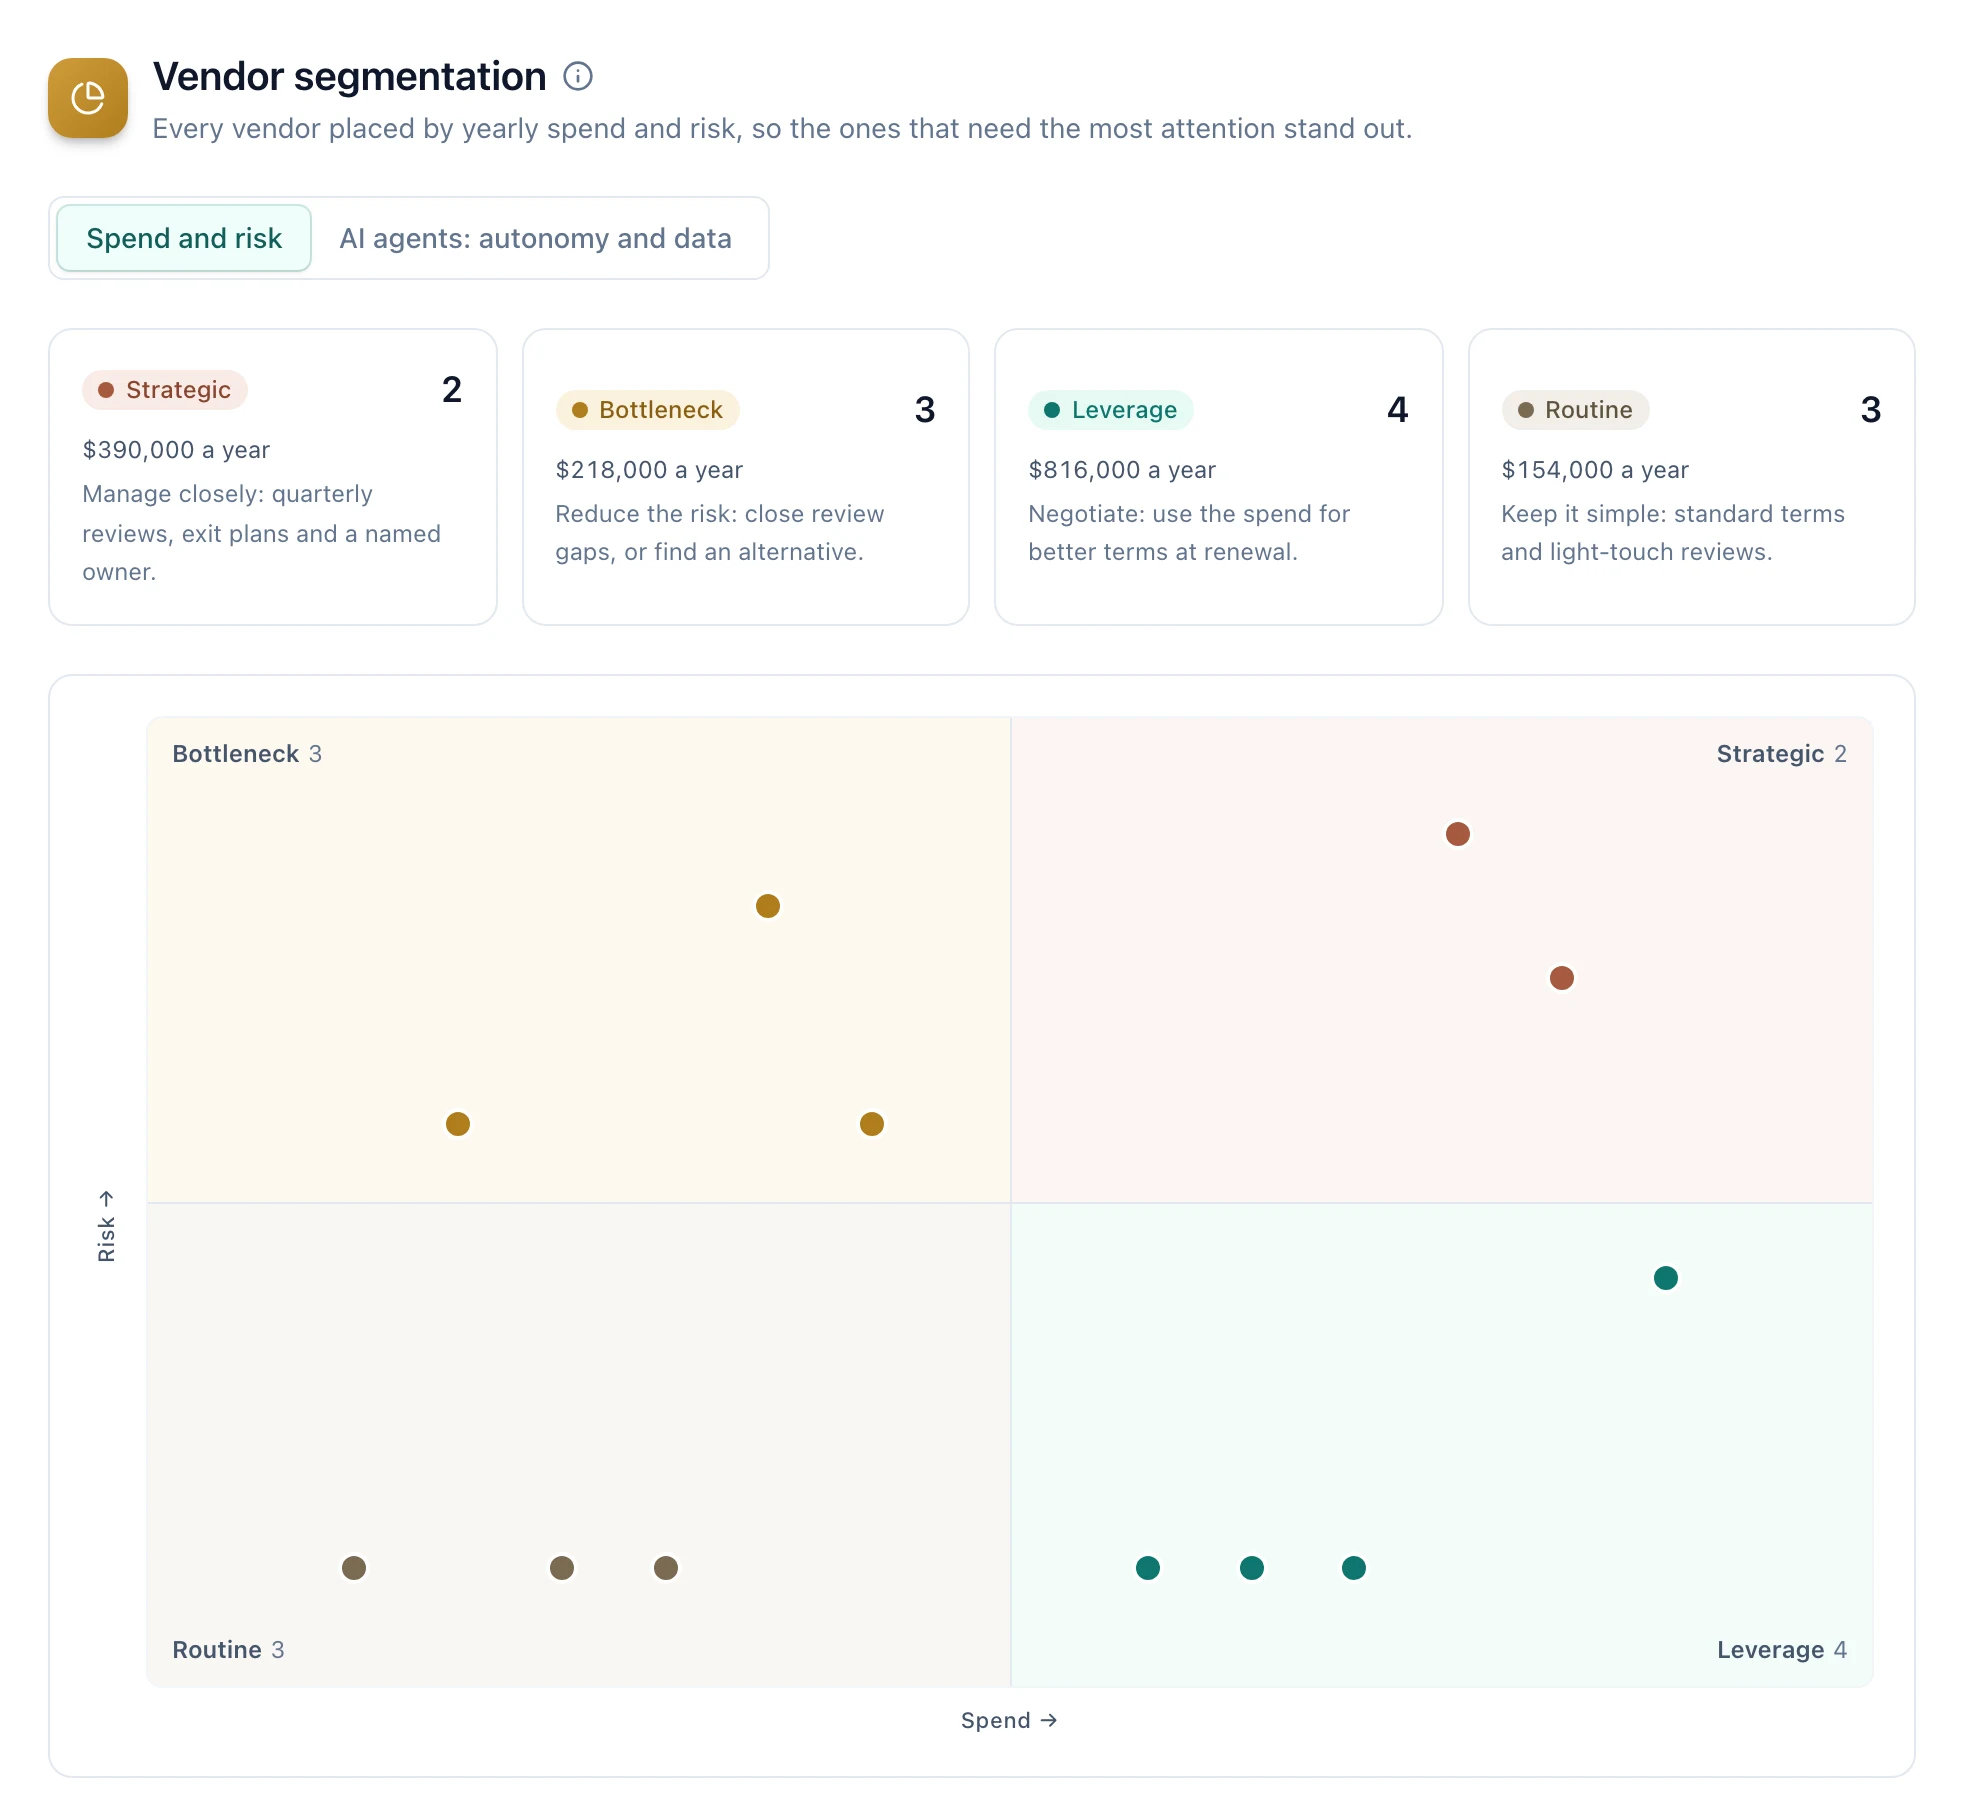
Every vendor placed by yearly spend and risk on one map, so the ones that need attention stand out instead of waiting to be found. Risk follows each vendor's risk badge, and vendors without a contract value are listed separately rather than guessed at.
Each quadrant comes with what to do next: manage Strategic vendors closely, reduce Bottleneck risk, negotiate on Leverage, and keep Routine simple. Click a quadrant to see its vendors and their spend.
Where every vendor stands, on one page
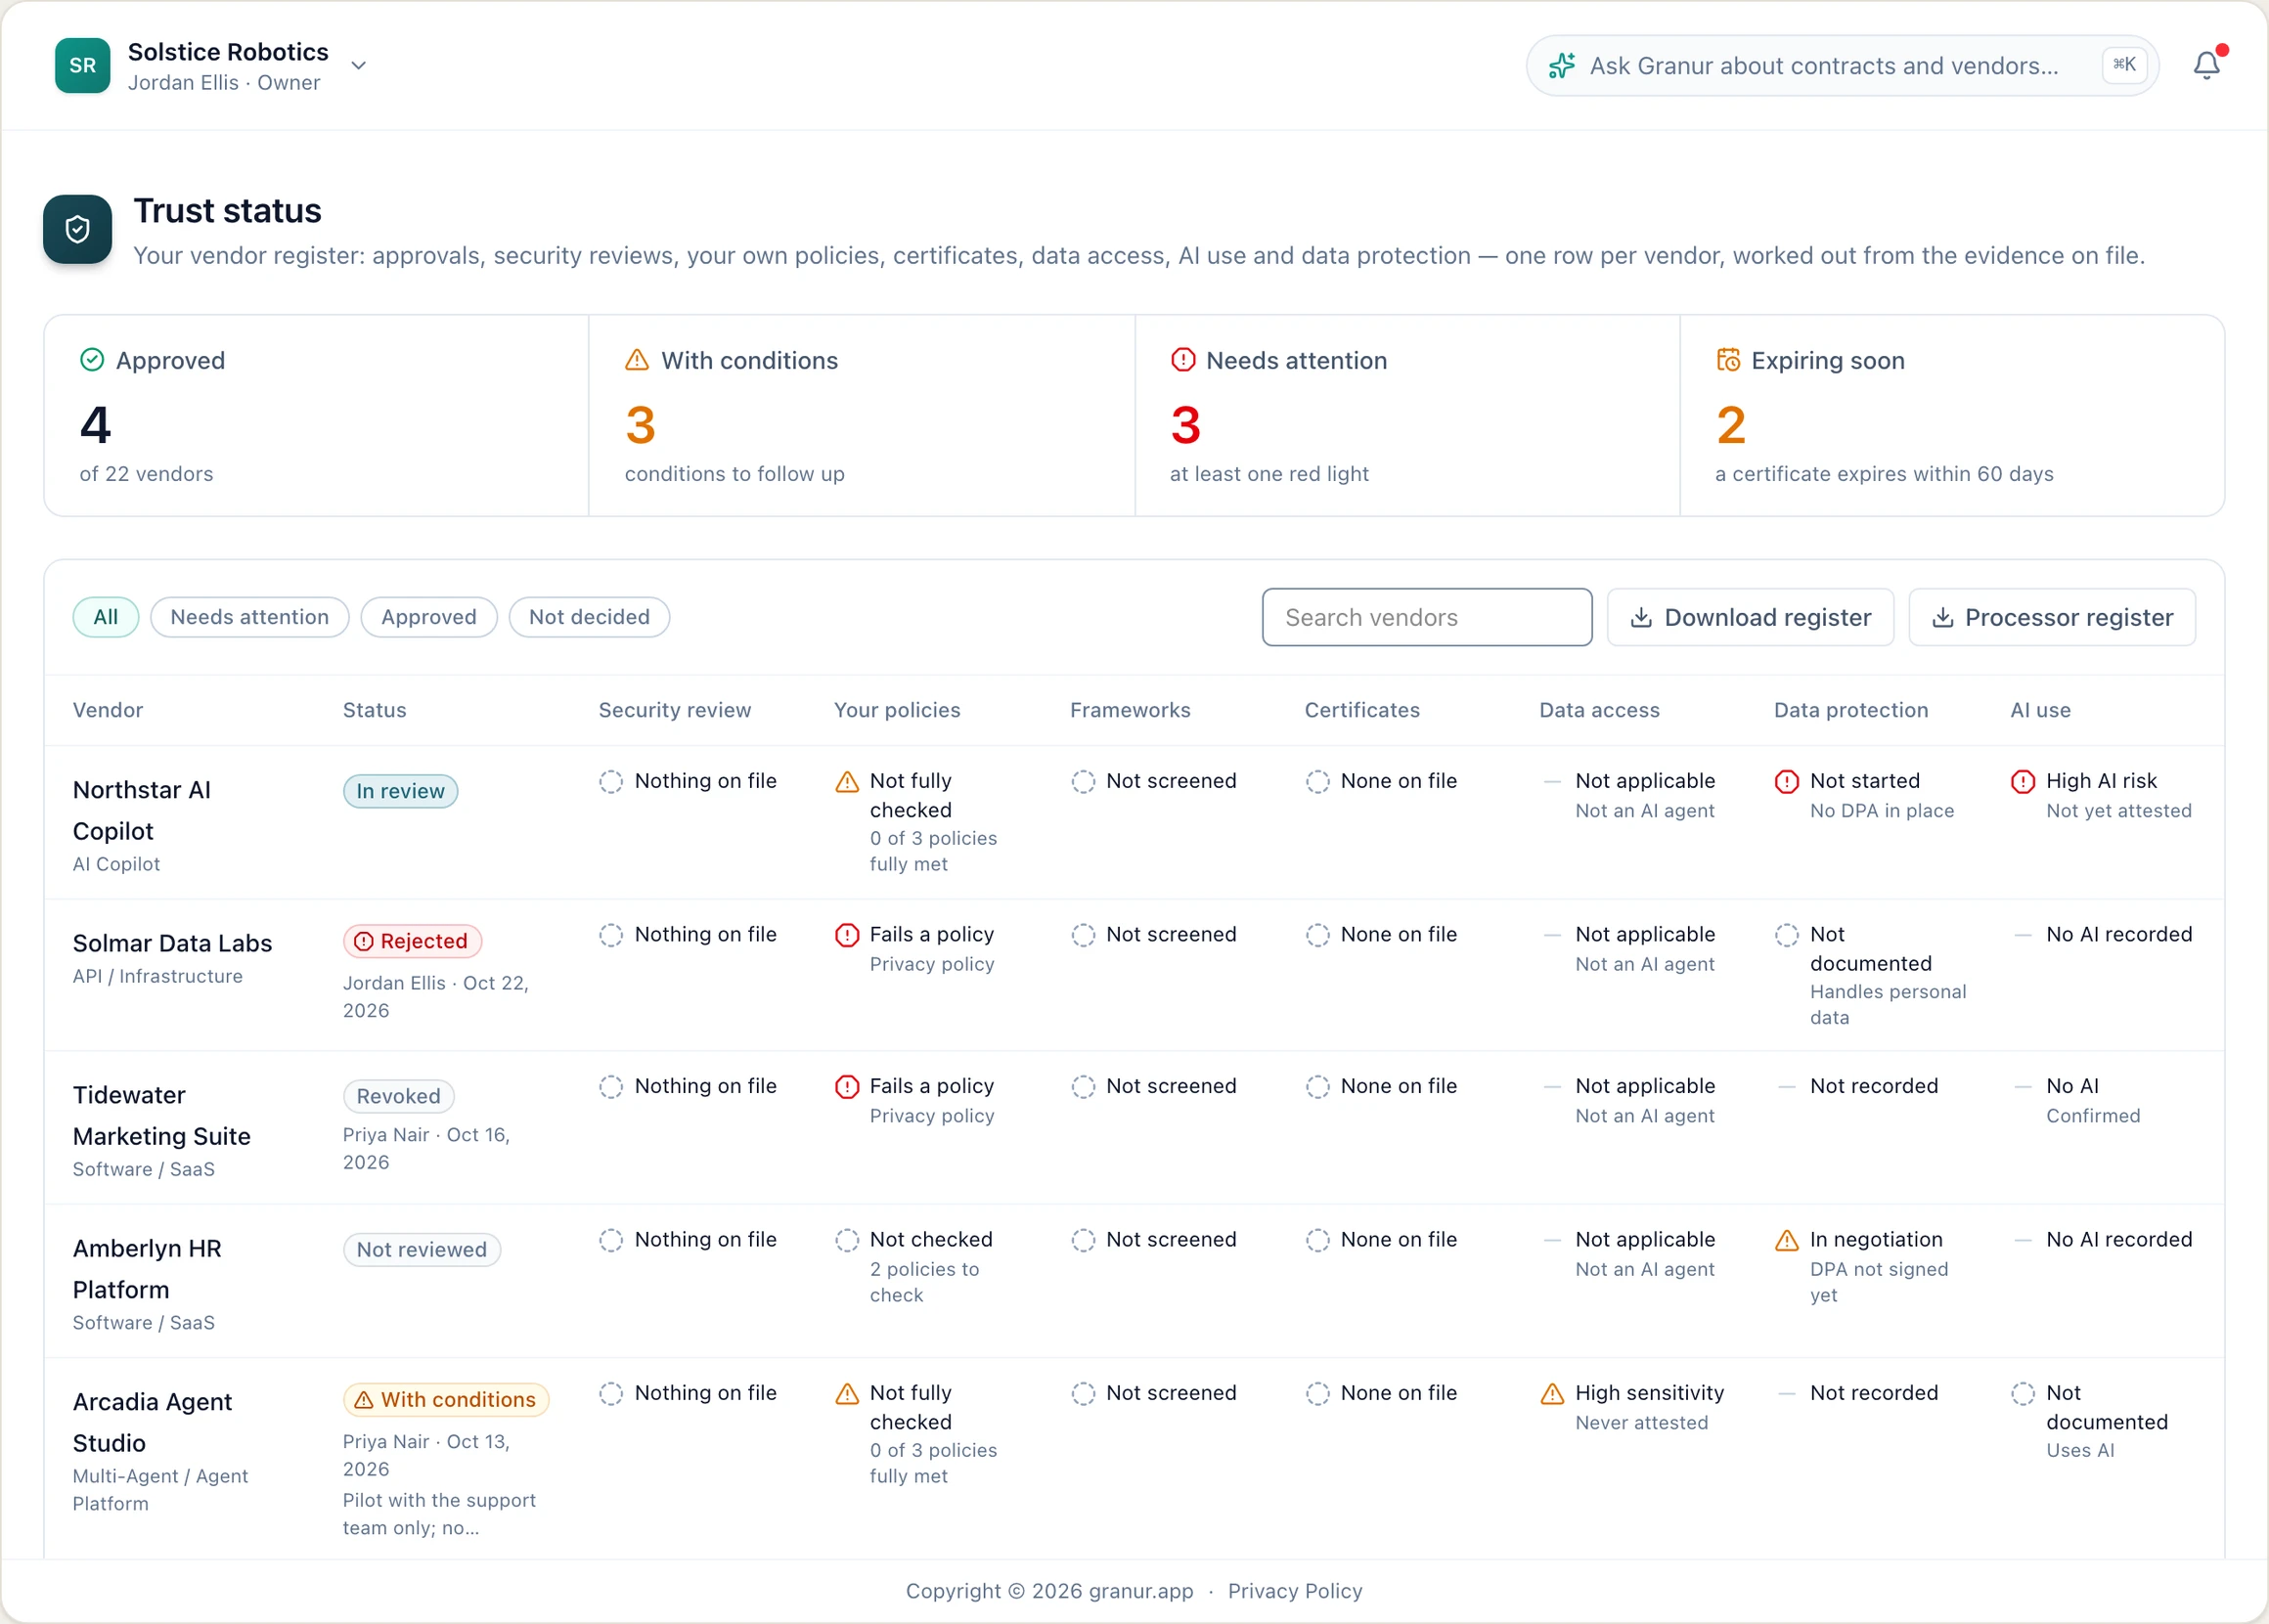
Approval decisions, security reviews, your own policies, certificates, AI use, data protection and AI-agent permissions — one row per vendor, worked out from the evidence on file. Nothing shows green without proof behind it.
Formal approvals, with conditions
Approve, approve with conditions, reject or revoke. Each decision records who made it and when, and the full history stays on the vendor's record.
Checked against your own policies
Add your privacy, AI and security policies as plain requirements, then check each vendor against the ones that apply — with a note on the evidence and a reminder to recheck after a year.
AI use on every vendor
Record what each vendor's AI does, whether it learns from your data and whether the contract makes it disclose AI. Every vendor gets an AI risk tier, vendors can answer a ten-question AI questionnaire through a secure link, and AI vendors are re-attested every year.
Data protection and DPAs
For every vendor that handles personal data: the data processing agreement, the categories of data, where it's stored and what covers transfers outside the EU/EEA. A missing DPA or transfer safeguard shows red.
A register ready for review
Filter to the vendors that need attention and download the register as a CSV, or the processor register — every vendor handling personal data, with its DPA, data categories, locations and safeguards — for your record of processing activities. A head start on DORA, NIS2, GDPR and SOC 2 reviews.
The relationship doesn't end at signature
A segmentation map tells you where to look. These are what you're actually looking at once you get there.
Health scorecards
A weighted KPI rubric — quality, delivery, cost, service, innovation, communication — scored by your team each period, with a suggested health rating and an action log. It stays internal: business reviews share the scores, never the reasons or your recommendation.
Business reviews (QBRs)
Quarterly for strategic vendors, less often for the rest. Granur drafts the agenda from the period — score trend, incidents, renewal and notice dates, expiring certificates — gives the vendor a pre-read without your internal notes, and keeps the decisions and a joint action plan with owners on both sides.
Obligations, not just renewals
The actual deliverables a vendor relationship promises — a report due quarterly, a right to audit, a volume commitment — tracked against an owner and a due date, separately from when any one contract with that vendor expires.
Certifications & insurance
COI, SOC 2, ISO 27001, ISO 42001, CSA STAR for AI, W-9, and anything else a vendor needs on file — tracked with expiry dates and an automatic amber-then-red warning as a certification approaches or passes expiration.
Vendor incidents, on the 72-hour clock
When a vendor reports a breach, log it on the vendor and Granur counts down the GDPR 72 hours to notify the authority. The clock stops when you record the decision, and running clocks show in everyone's notifications.
Onboarding, tracked to go-live
A five-step technical checklist — system and data access provisioned, integrations and data feeds configured, the team trained, go-live confirmed, Technical Owner sign-off — started the moment a contract is executed, so implementation has an owner and a record instead of stalling in someone's inbox.
Offboarding, checked off
A five-step checklist — access revoked, data returned, final invoice, knowledge transfer, contracts closed — so winding down a vendor relationship is a record, not a memory.
Agent permissions & re-attestation
For a vendor onboarded as an AI agent, a living record of what it's actually authorized to access and do — data scopes, data sensitivity, which actions it takes autonomously versus which need approval, model version — reviewed on a recurring cadence with an amber-then-red badge as re-attestation comes due, so authorization is confirmed on a schedule instead of set once and forgotten.
Vendor management is half the picture. See the dashboard where every contract is tracked, stage by stage
Your vendor data, isolated and accounted for
Granur is early — we're straightforward about what's built today rather than borrowing badges we haven't earned.
Org-scoped multi-tenancy
Every contract, user, and event is scoped to your organization — no cross-tenant access.
Hashed credentials, session auth
Passwords are hashed, never stored in plain text; sessions are signed and short-lived.
Full, exportable audit trail
Every stage move, approval, and settings change is logged automatically — visible on the Timeline, and exportable as a CSV or PDF for a security reviewer.
You control the data
Your vendor data lives in your own database — Granur doesn't share it across organizations.
See your own vendors on the pipeline
Pick a plan, upload a handful of agreements, and watch the evaluation scorecard and health tracking fill in.