

Every contract, tracked stage by stage, tied to the vendor it belongs to
Eight stages, five parallel review tracks and three compliance gates, on one dashboard and tied to each vendor's record.
Every contract, one centralized view
A Kanban board or a sortable table — the Contract Log — your choice, showing every contract at whatever stage it's actually in, right now. Not a status someone updates when they remember to; the real, current state of the whole pipeline, in one place.
Every stat tile on the dashboard is a live filter, not a static number. Click Critical tier, New vendors, or a specific contract type, and the view narrows to exactly that slice — no separate report, no exporting to a spreadsheet to answer a simple question.
Click any tile to filter the board to exactly that slice.
Eight stages that move it forward
Every vendor relationship carries a stage, and every stage change is timestamped — so “where is this?” is always a one-second answer. Eight of them are forward motion — a contract actively moving through review, approval, and on into active management and renewal. “With Vendor” and “Hold” are wait states, not part of that flow — a contract can sit in either from any point and come back. This is the default — an account owner can add, reorder, rename, or remove stages from the workflow builder, no code change required — guided by industry best practices for securing contracts and vendor relationships, not locked in as one-size-fits-all.
A first-time tech platform, data vendor, or AI agent sees Evaluation and Security & Compliance move to the front of this order, ahead of Business & Finance Approval and Legal Review — a renewal keeps the order shown below.
Capture the business need, use case, scope, vendor, owner, and initial requirements.
Assess solution fit, capabilities, architecture, commercial model, and alternatives.
Review security, privacy, data handling, regulatory requirements, and third-party risk.
Review and negotiate contract terms, liability, IP, termination rights, and legal requirements.
Confirm business sponsorship, budget, financial commitments, and required leadership approvals.
Route the finalized agreement to authorized signatories and complete execution.
Manage the contract, vendor relationship, usage, spend, performance, and obligations.
Review continued need and performance, then renew, renegotiate, replace, or terminate.
Five tracks, tracked independently
A vendor relationship's overall stage tells you where it sits in the pipeline. But Engineering, the Business Owner, Finance, Legal, and Security each move at their own pace — so Granur tracks each one separately, with its own reviewer and status, instead of flattening everything into a single “in review” flag.
Legal gets a deeper status vocabulary than the other tracks — including Send to OC, With OC for Review, and Review OC Feedback — to reflect outside-counsel handoffs without inventing a separate workflow for it.
Three gates, before anything moves
New-vendor and uses-AI flags trigger the gates automatically — nothing relies on someone remembering to ask. Start with these three, or set your own in Settings.
Every contract also carries its own automatic risk score — new vendor, missing diligence, high value, urgent — visible at a glance on the dashboard, not something you have to go looking for.
Vendor Risk Assessment
Every new tech platform, data vendor, or AI agent is screened before a contract can move through review.
Privacy / AI diligence
Flagged automatically for any agreement involving personal data or AI usage.
Vendor Request Form
The formal intake record required before procurement and finance engage.
Upload a PDF, not a blank form
Drop in a contract and AI reads it — pulling out the terms that matter and pre-filling the intake form for you to review and correct, not blindly trust. Nothing saves until you confirm it.
Reading contracts is the tedious part — let AI do that part
Intake extraction is one job. Two more run the same way — scoped narrowly, reviewed by a person, never auto-applied without a look.
Risk-clause review, on demand
Run an AI pass over the actual contract text and get back specific, severity-tagged flags — an uncapped liability clause, a silent auto-renewal, one-sided indemnification — each with the exact excerpt it came from, not a generic warning. It also reads the contract's AI terms (whether the vendor must disclose AI use, and whether it may train on your data), and the clause library suggests AI clauses to close the gaps.
Ask your contracts a question
“Which vendors renew in Q1 with an auto-renewal clause?” Ask it directly and get an answer with the specific contracts it's based on — instead of opening ten agreements to check.
Where the deal stands, not just where the document is
“In Legal review” tells you the redline is being worked. It doesn't tell you whether you're close on price, still fighting over liability caps, or waiting on the vendor to counter. Best-practice CLM keeps those as separate questions — so Granur tracks negotiation as its own record on every contract: status, how many rounds it's taken, where the current position sits, what outcome you're targeting, and the next concrete step.
It updates independently of the Legal track, so a deal can be “Final Terms” on negotiation while the redline is still in a review round — an accurate picture instead of one flattened status.
Every date, every change, one chronological view
Key dates — submission, start, end, deadlines, redlines-to-vendor, effective, and renewal — sit alongside a live log of stage moves and review-status changes, split into what's upcoming and what already happened.
Context stays on the record, not in someone's inbox
Why a deal stalled, who flagged a risk, what was decided and why — that's exactly the kind of thing that gets lost in an email thread six months later.
An activity feed, not a status meeting
System events and team posts in one reverse-chronological feed — what changed, who posted about it, and who liked or replied — instead of a recurring sync to cover the same ground out loud.
Comment and @mention, right on the record
Ask a question or loop someone in directly on a contract or a vendor thread — they're notified, and the exchange stays attached to the thing it's actually about.
Notifications ranked by what matters
Renewals, deadlines, mentions, and stuck-in-stage contracts — ranked by severity in one bell icon, instead of an inbox where an urgent flag looks the same as a newsletter.
An executed contract still has a job to do
Signing a contract isn't the finish line — the deadline it creates and the spend it represents still need tracking afterward.
Reminders that find you
A personal email or push reminder ahead of any renewal or deadline, on your own lead time, plus a private calendar feed of every deadline and open obligation you can subscribe to from any calendar app.
Spend, sliced every way
Portfolio value, average deal size, and spend broken down by vendor, type, and stage — plus which renewals in the next 90 days carry the most risk, without exporting anything to a spreadsheet first.
No surprise auto-renewals
Two renewals, two outcomes: one contract cancelled cleanly before its notice deadline, one renewed with the right reviews and a fresh look at the terms.
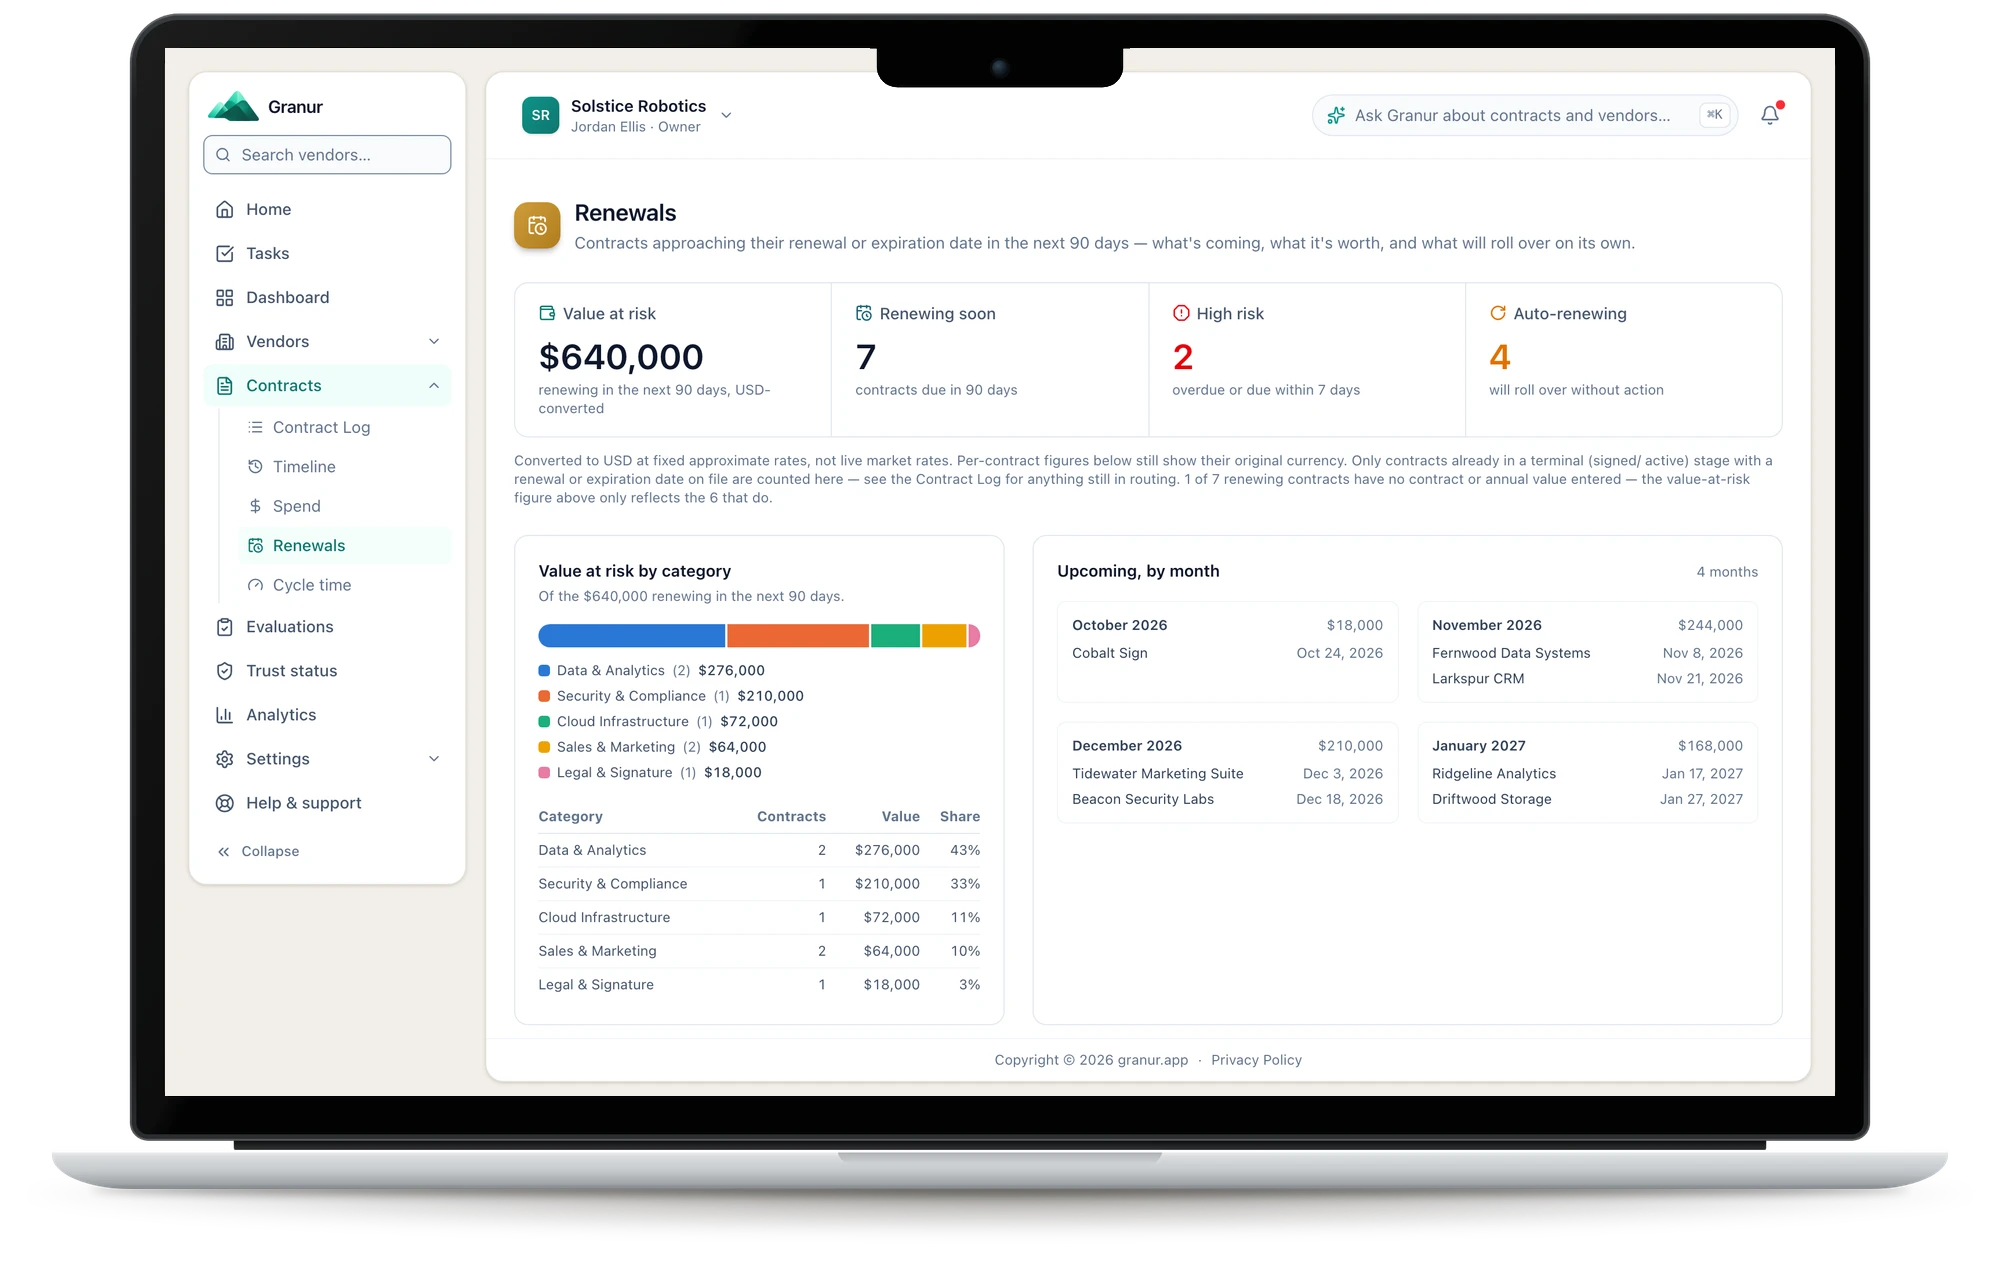
Every renewal in one list
Every contract that renews or ends is listed with its date, value, risk and whether it renews on its own, plus what's coming up by month. One click opens the renewal decision.
The pipeline moves things forward without being asked
A tracker only helps if someone remembers to check it. Granur also pushes.
Automation rules
When a contract enters a stage, or a checklist finishes, a rule can notify Slack or move the contract forward on its own — no one has to remember to trigger it.
Slack, Teams & webhooks
A daily digest or an on-demand push to Slack or Teams, and outbound webhooks for your own systems — a contract created, a stage changed, a signature completed — signed and delivered automatically.
A read API of your own
A dedicated API key gives another internal tool read access to your contract data — no export, no copy-paste, no waiting on someone to pull a report.
Every contract here is tied to a vendor relationship. See the vendor directory, evaluation scorecards, and health tracking
Contract data follows the same security model as everything else in Granur — org-scoped multi-tenancy, hashed credentials, and a full, exportable audit trail. See how vendor and contract data is secured
See your own contracts on the pipeline
Pick a plan, upload a handful of agreements, and watch the routing map fill in.